Description
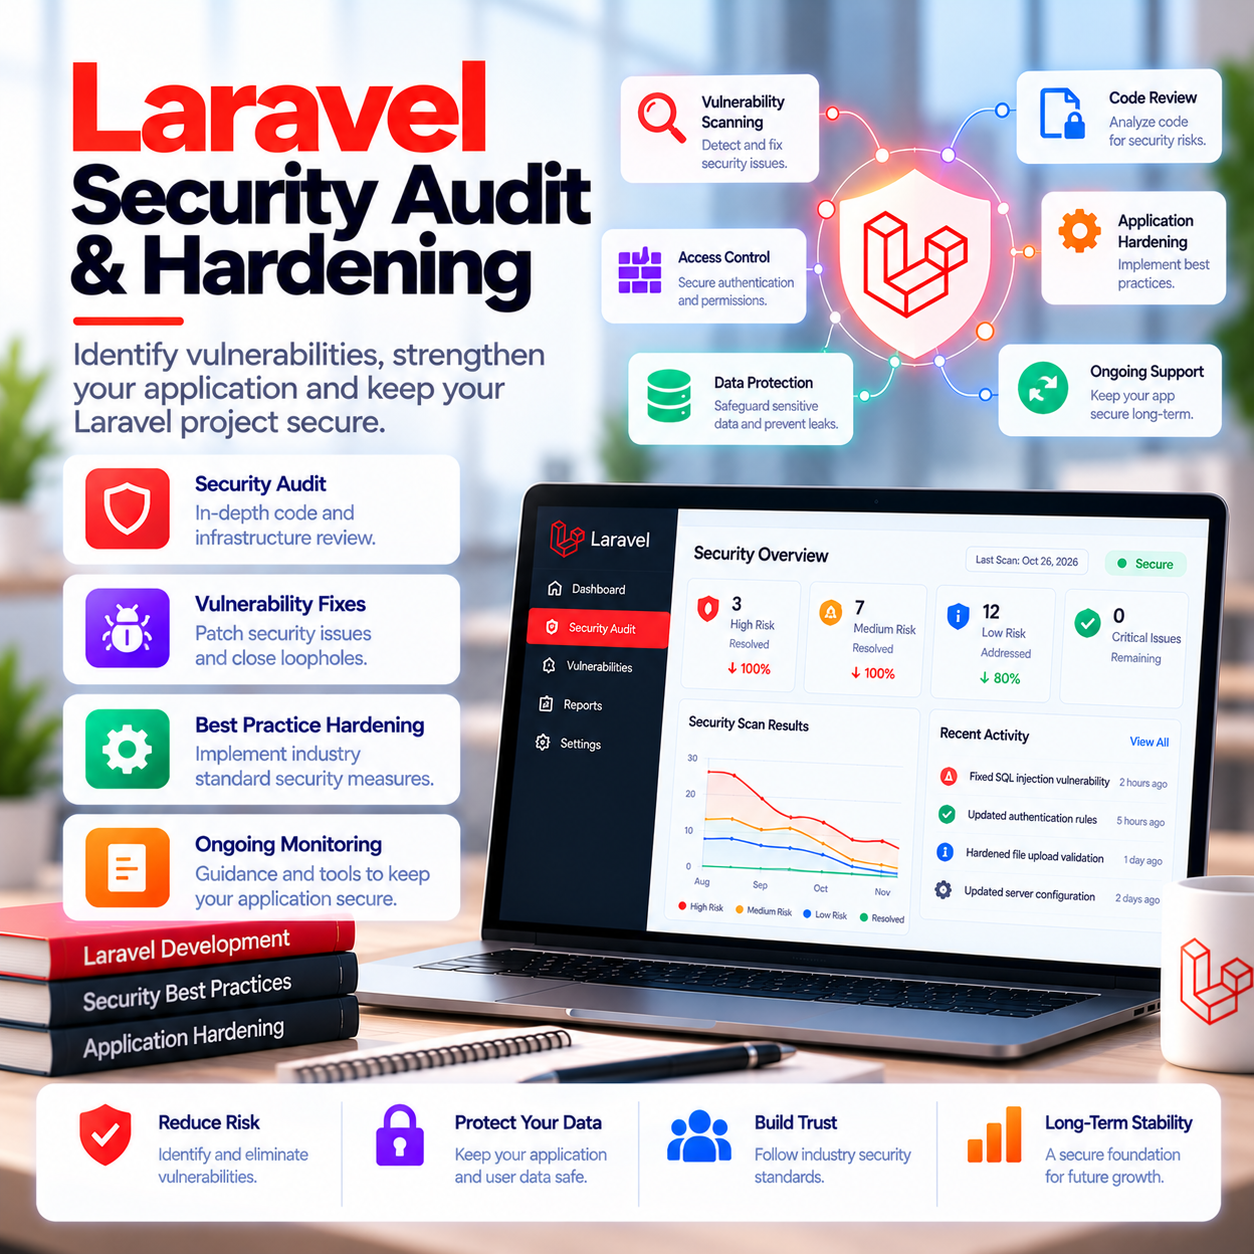
Get a structured review of the security areas that matter most in a Laravel application before a launch, after a major change, or when risk is unclear.
What this helps you achieve
- Find avoidable exposure in authentication and permissions
- Review APIs, validation, uploads, and sensitive data handling
- Identify risky configuration, secrets, and dependency issues
- Strengthen security controls before they become expensive incidents
- Give your team a prioritised remediation plan
What we deliver
- Application security scope review
- Authentication, authorisation, and role checks
- Input validation, file uploads, APIs, and common attack surfaces
- Dependency, configuration, and secret-handling review
- Findings report with severity, recommendations, and retest options
Choose the right package
| Package | Best for |
|---|---|
| Starter | A focused review of authentication, permissions, configuration, and high-risk application areas. |
| Standard | A broader audit covering APIs, uploads, dependencies, data access, and targeted hardening work. |
| Premium | A deeper security engagement with expanded testing, remediation support, retesting, and a detailed hardening roadmap. |
How it works
- Understand the application, users, data, integrations, and risk priorities.
- Review code, configuration, access paths, and representative workflows.
- Document findings and apply the agreed hardening improvements.
- Retest the updated areas and deliver a clear remediation summary.
Who this is for
businesses preparing a Laravel application for launch, handling sensitive data, or inheriting an application with unclear security controls.
Important: This is a focused application security service, not a guarantee of complete security or a substitute for a regulated penetration test where one is required.
Ready to get started? Choose the package that best matches your current scope. After checkout, we will confirm your goals, access requirements, technical context, and delivery plan before implementation begins.